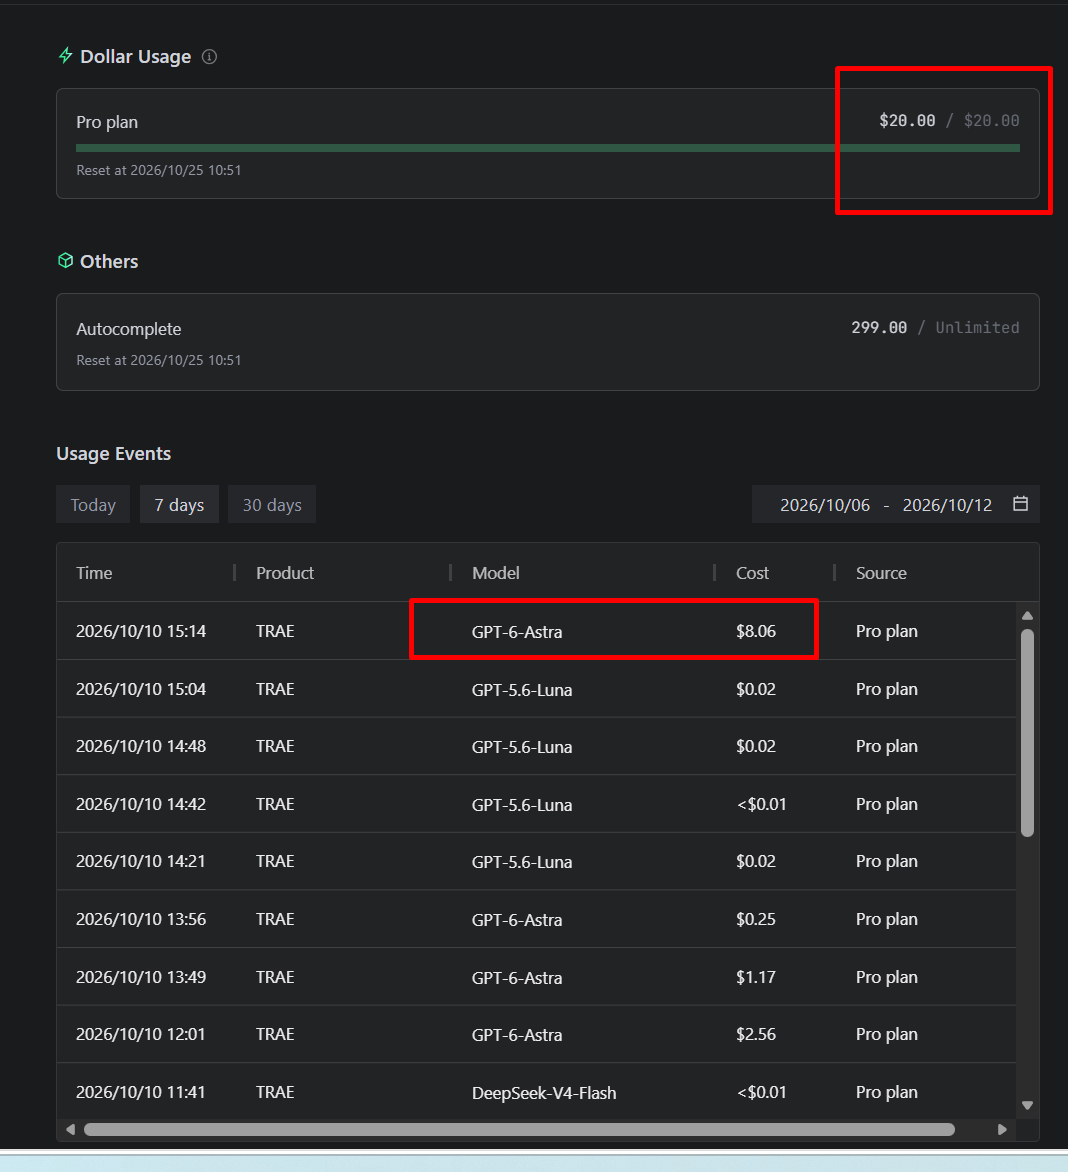
Debug 一个小问题,就把Token耗光了?是否无限循环调用了呢?
之前有人告诫Astra 会炸光流量,我还以为是极个别呢 ,提交了反馈,没有收到回信;
我的UID:7473376495643509768
同样的错误再次出现,说明上一轮路径修复没有解决实际执行问题,抱歉让你又构建了一次。这次先暂停发布,我会检查 Windows 到 SSH 的命令传递和远端实际工作目录,用只读探针复现后再修复,不运行迁移或切换服务。
Evaluating budget and transport issues
I’m noticing that we have about 24k remaining in the budget. I think we need a solid fix for the transport issues, especially related to bash stdin and compose root lock. It seems crucial to thoroughly inspect our skills with the debugger, especially since this has come up repeatedly. I have to ensure we cover all the necessary aspects. Is there anything else we should focus on with this budget?
我会按 TRAE-debugger 收集运行证据,再用 test-driven-development 补行为回归测试。本次会话记为 release-ssh-path,验证三个假设:
- Windows SSH 调用丢失了
bash -c的引号,导致cd和环境变量未作用于部署进程。 - 生产配置文件确实缺失或不可读。
- 暂存 Compose 的相对路径被解析到了暂存目录,而不是生产目录。
总结
调试只收集路径和退出码,不读取密码;你也可以随时要求中止。
只读探针已复现问题:执行了嵌套 bash -c "cd ..." 后,远端目录仍是 /home/appadmin,而 .env.production 和暂存 Compose 都可读。也就是说,文件没有丢,上一轮新增的引号在 Windows SSH 参数传递中失效了。
我会改为通过标准输入传送脚本,避免嵌套命令引号;同时固定 Compose 的项目目录,防止它把 ./logs 等路径解析到暂存目录。
Estimating token budget
I’m estimating my token budget and wondering if I have the right figures. I started with around 29,000 tokens but now it seems like I might have about 27,000 remaining. I’m calculating, and with the adjustments, I think I’m down around 25,000 tokens. I need to keep track of this closely to ensure I have enough for my needs. Let’s hope I can manage this effectively!
Updating infrastructure tests
I’m considering the need to upgrade old tests without mutating the infrastructure stage. It’s vital that I address all relevant tests, especially focusing on the appropriate ones. I won’t ignore any of them, but I will need to update them to reflect the new naming conventions and ensure a better structure. I think the first thing I need to tackle is the runtime aspect to keep everything functioning smoothly!
Investigating SSH Encoding Issue
I’m looking into a potential bug with actual Windows PowerShell (WPS) piping to SSH. The issue seems to involve the Byte Order Mark (BOM) not being present when encoding, yet the SSH server might be reading it. It’s known that Windows OpenSSH can encode Unicode stdin with BOM. I need to gather evidence to verify this, like using od -An -tx1 to read and capture the payload bytes from WPS.
运行测试又发现了一个兼容性问题:在独立的 Windows PowerShell 5.1 进程中,标准输入会被加上 UTF-8 BOM,Bash 因而在第一行失败。我会把脚本编码为 Base64 后传给 SSH,由远端解码执行,避开引号和 BOM 问题;仍会用真实 SSH 验证,而不只检查脚本文本。
Investigating command outputs
I’m trying to understand why the command returns 0. I’m looking into details like the printf command, Base64 processing, and ssh with -EncodedCommand. I also need to consider how powershell.exe handles CLIXML output serialization. It seems important to inspect stderr output because there’s a mismatch where no output is printed for stdout. There are quite a few moving parts here, so I’ll need to break this down step by step to clarify!
Debugging SSH Bug
I’m looking into a bug with native SSH in PowerShell and specifically checking if the $payload variable includes the correct interpolated value. I want to test and debug various byte strings to see what gets printed. I should also ensure there’s no sensitive information being exposed in the process. It’s crucial to keep everything secure while figuring this out! Let’s keep monitoring those hashed values carefully.